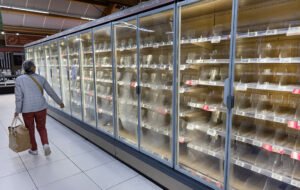
Fridge hack costing thousands and thousands and sparking fires stemmed from poor safety
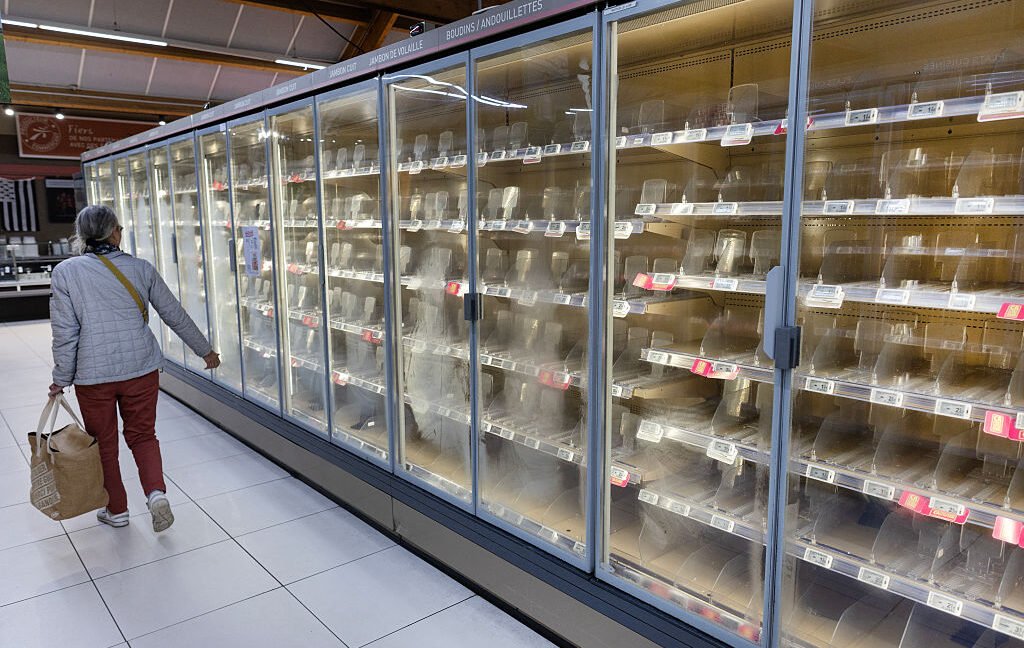
Moreover operating controllers with outdated firmware, the affected shops seemingly additionally didn’t put the gadgets behind a VPN and create a restricted record of IP addresses allowed to log in. These protections are customary however typically not adopted. On this case, that failure enabled a mass hack that seemingly value tens or lots of of thousands and thousands of euros. Spain, Portugal, Poland, Germany, and Belgium have been additionally reportedly affected.
“Two issues would have modified the result,” researchers at Pen Take a look at Companions stated Wednesday. “Cyber hygiene would have prevented the entry: take the controller off the general public web, put distant entry behind a VPN and an IP allowlist, convey third-party package onto the community in a managed, owned and documented approach reasonably than leaving it on a contractor’s personal connection, change identified and default credentials, and patch to a present launch.”
Researchers from safety agency Claroty warned of the specter of ignoring these commonsense steps final October. The US Cybersecurity and Infrastructure Safety Company did the identical in February.
In an electronic mail, Copeland acknowledged a vulnerability “recognized in a discontinued, end-of-life technology of controllers” and stated the corporate is working with clients to stop comparable incidents sooner or later. Danfoss representatives didn’t instantly reply to questions. CNN stated the corporate additionally cited discontinued fashions.
Thus far, the get together behind the assault has remained silent. That raises the likelihood that the motive was vandalism on a mass scale. One other risk is a nation-state or different worldwide actor aiming to create a continent-wide disruption.
The incident underscores the stress between the monetary and safety departments in most companies. Some firms are loath to spend massive sums of cash on new tools when there aren’t any tangible advantages or financial savings. Solely after a devastating hack do they notice why the funding was worthwhile. Executives at affected grocery store chains will seemingly be taught the laborious classes. Much less clear is whether or not the cautionary story will sway different companies.